
Governance & Economic
The Company operates the business with transparency, accountability, and the respect for the law.
The Company promotes the acts of fraud prevention and anti-corruption in line with prioritizing the Personal Data Protection and Cyber Security.
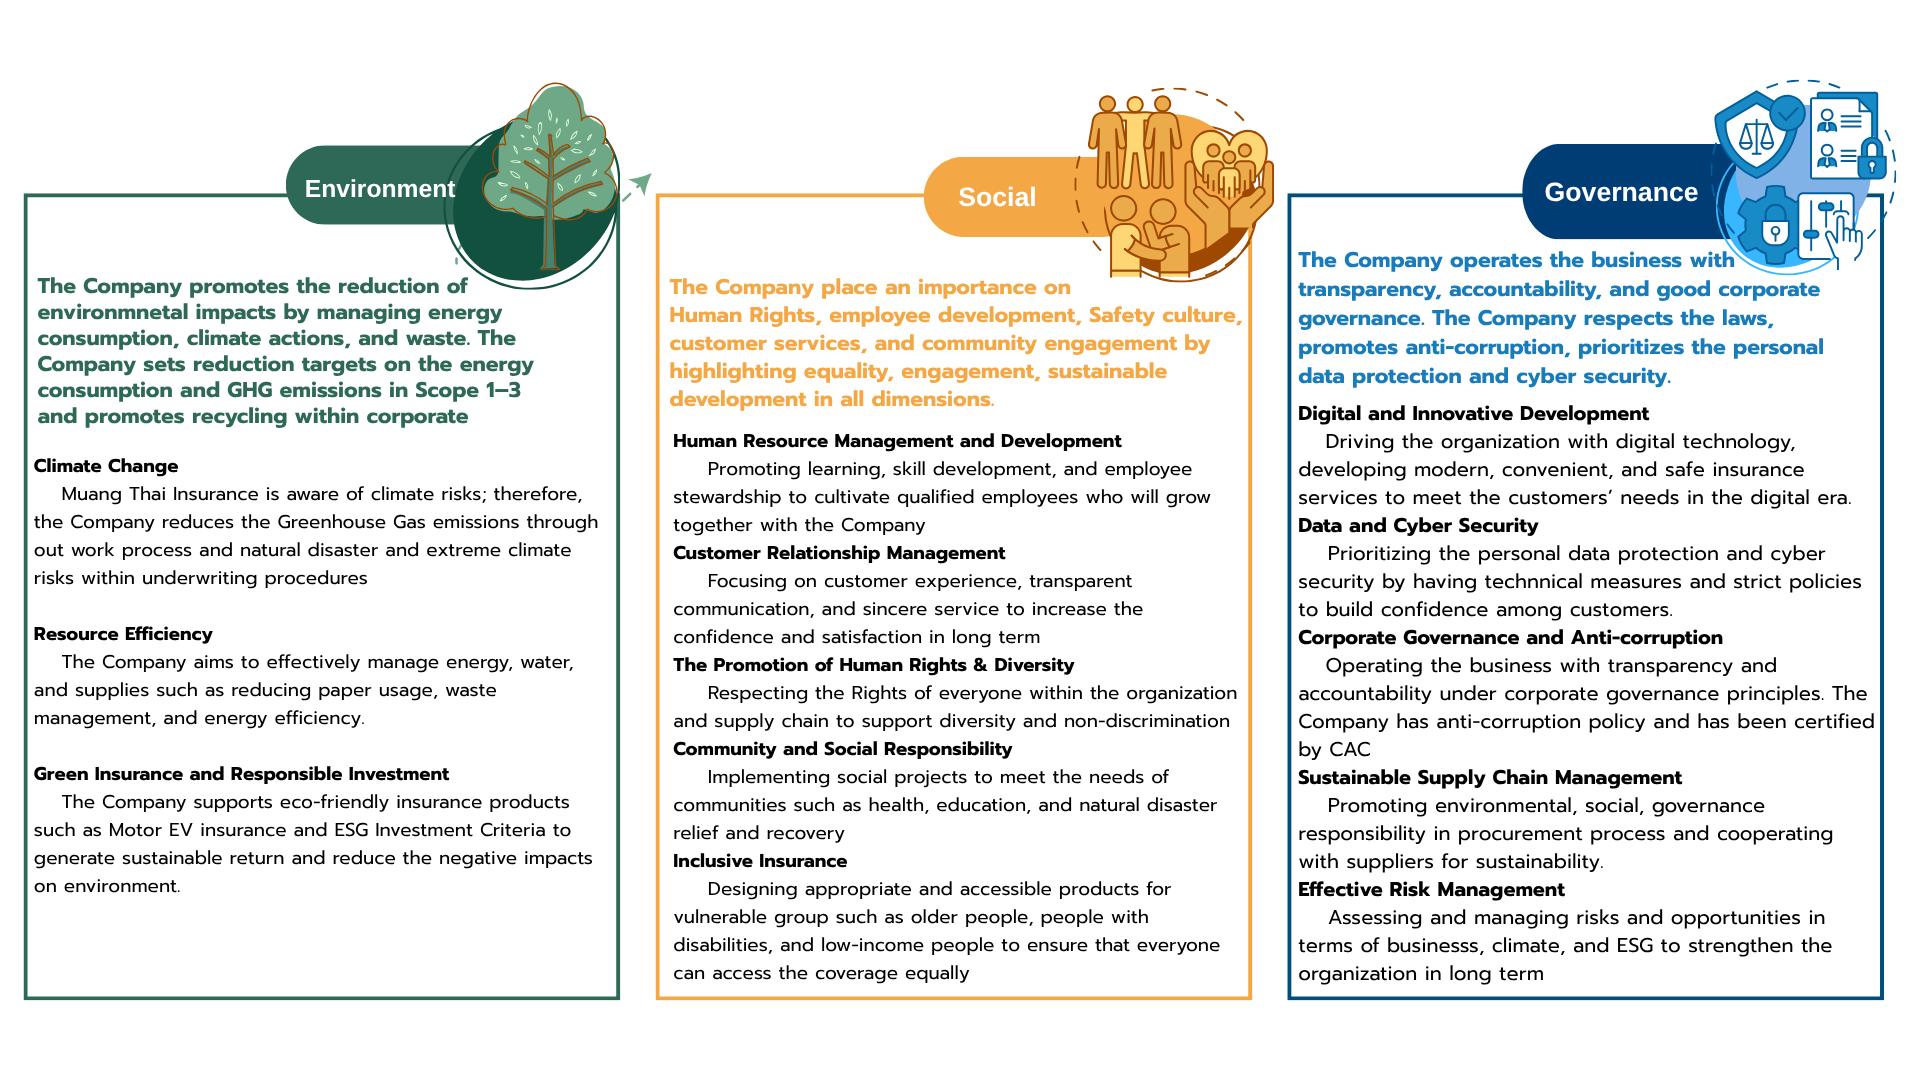
Muang Thai Insurance Public Company Limited recognizes that conducting business under the principles of good corporate governance is the fundamental foundation for stability, credibility, and sustainable long-term growth. The Company prioritizes transparent governance, holistic risk management, digital and innovation development, data protection and cyber security, as well as sustainable supply chain management in order to build confidence among customers, shareholders, investors, suppliers, and all groups of stakeholders. Moreover, the implementation in governance and economic dimension can enhance the competitiveness, reduce business risks, prepare the readiness for economic, technological, and regulatory transformation. This also supports the stable and sustainable economic growth of the Company and society in long term.
Policy
The Company operates the business under corporate governance principles, transparency, responsibility, and accountability by integrating ESG with corporate strategy and risk management process at all levels. In addition, the Company promotes the use of digital technology and innovation to improve the work efficiency and enhance the customer service in alignment with personal data protection and cyber security according to international standards. The Company has Fraud Prevention and Anti-corruption Policy under No gift Policy principles and leverages the ethical business conduct. Sustainable supply chain management guidelines are established to encourage the systematic Enterprise Risk Management and the compliance with Human Rights Principles, laws, and ESG standards among suppliers in order to maintain financial stability, build the stakeholders’ confidence, and support the Company’s sustainable growth in long term.
| SDGs | SDGs Target | MTI Target | Performance in 2025 |
|---|---|---|---|
| SDG 8 | Promoting sustainable economic growth, productive employment, and stable organization | Effectively managing corporate risks and maintaining financial stability and sustainable growth | Capital Adequacy Ratio (CAR) higher than the OIC’s criteria No incident affecting the financial stability Risk Management system covers climate risk, cyber risk, and ESG risk |
| SDG 9 | Developing infrastructure, innovation, and technology to enhance economic efficiency | Driving digital transformation and InsurTech to boost the work efficiency and customer service | Developing Muang Thai Friends Application, E-policy, Online Claim, AI and Automation for underwriting and claim The Application has 77,535 installs |
| SDG 12 | Ensuring responsible production patterns and consumption, including sustainable supply chain | Developing transparent procurement system and enhancing suppliers’ operation according to ESG criteria | Assessing 71 critical suppliers according to ESG criteria, and 100% of suppliers passed the assessment No critical ESG risks from suppliers Promoting E-policy and digital transformation to improve resource efficiency |
| SDG 16 | Promoting transparent organization with governance, anti-corruption principles, and rights protection | Cultivating corporate governance, anti-corruption, data protection, and transparency in business operation | Receiving SET ESG Rating at AAA level, CGR 5 stars, and CAC Certification No corruption case No conflict of interest No data breach (0 case) |
| Target | Performance |
|---|---|
| No conflict of interest | 0 case |
| No corruption case | 0 case |
| Employees acknowledge Corporate Governance and Anti-corruption Policies | 100% |
| No data breach or loss | 0 case |
| No complaint regarding personal data protection | 0 case |
| Critical Suppliers ESG Assessment | 100% |
Muang Thai Insurance place an importance on Good Corporate Governance, transparency, legal compliance, and stakeholder responsibility under strong governance principles. The Company is committed to operating the business with honesty and accountability and adhering to ethic standard to support the long-term sustainability in environmental, social, and economic stability.
Corporate Governance and Anti-Corruption
Importance
Good Corporate Governance and Anti-Corruption are fundamental foundation for insurance company to build confidence among stakeholders such as customers, employees, suppliers, shareholders, and regulators. Insurance is a business that requires trust, transparent management, accountability, and must diminish mutual interests to maintain the Company’s stability in long term.
Additionally, the legal compliance and corporate governance principles can reduce reputation risks, regulatory risks, and financial risks, as well as enhancing corporate image as a business with ethics and social responsibility.
ESG Governance at the Committee level to Operational level
with the details of responsibilities
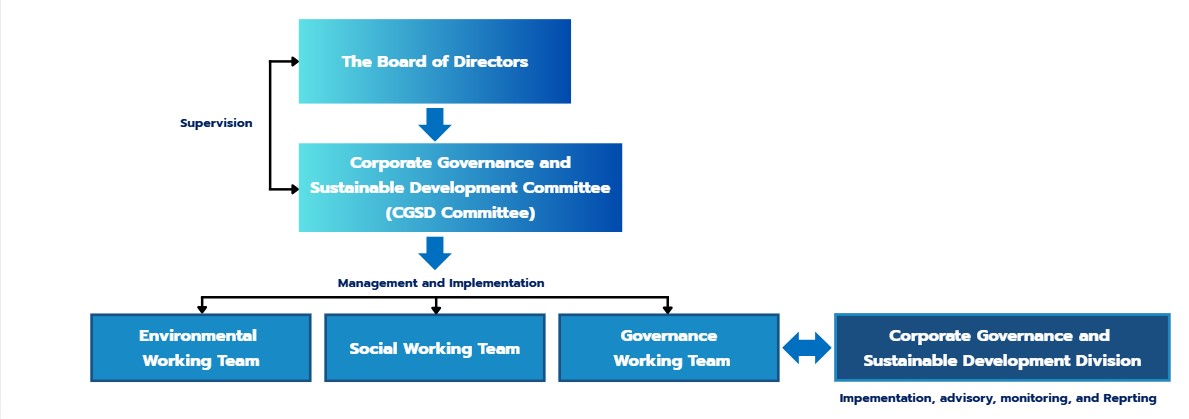
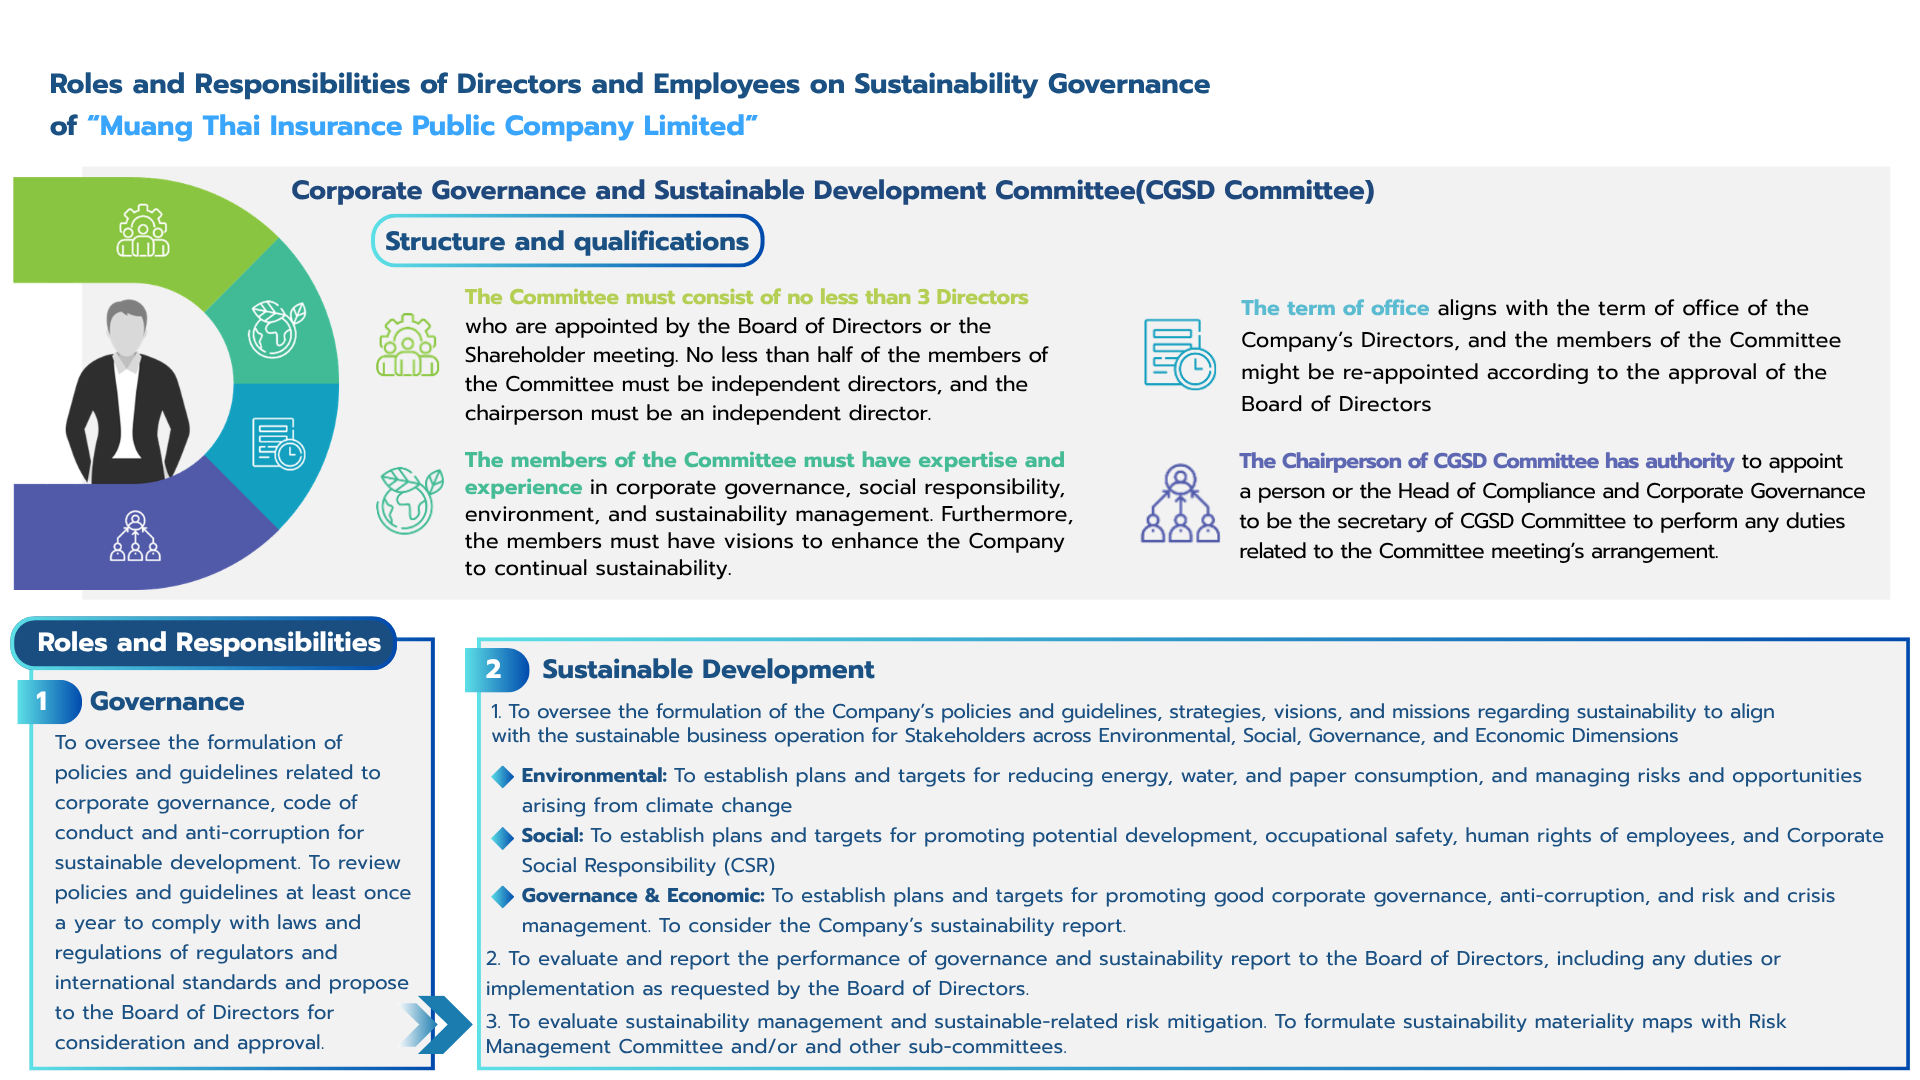
The Company established Corporate Governance and Sustainable Development Committee (CGSD Committee) according to the resolution of the Board of Directors on February 27, 2024. The Committee has duties to supervise the strategic directions and goals based on the Company’s Sustainability policies and framework, provide opinions and suggest sustainability management guidelines to the working teams and relevant departments. In addition, the Committee is responsible for monitoring, considering, and reporting the performance to the Board of Directors to ensure that the Company operates the business with social responsibility, transparency, and fairness, reassure all stakeholders’ confidence, and enhancing the Company to the sustainable growth.
Good Corporate Governance Structure
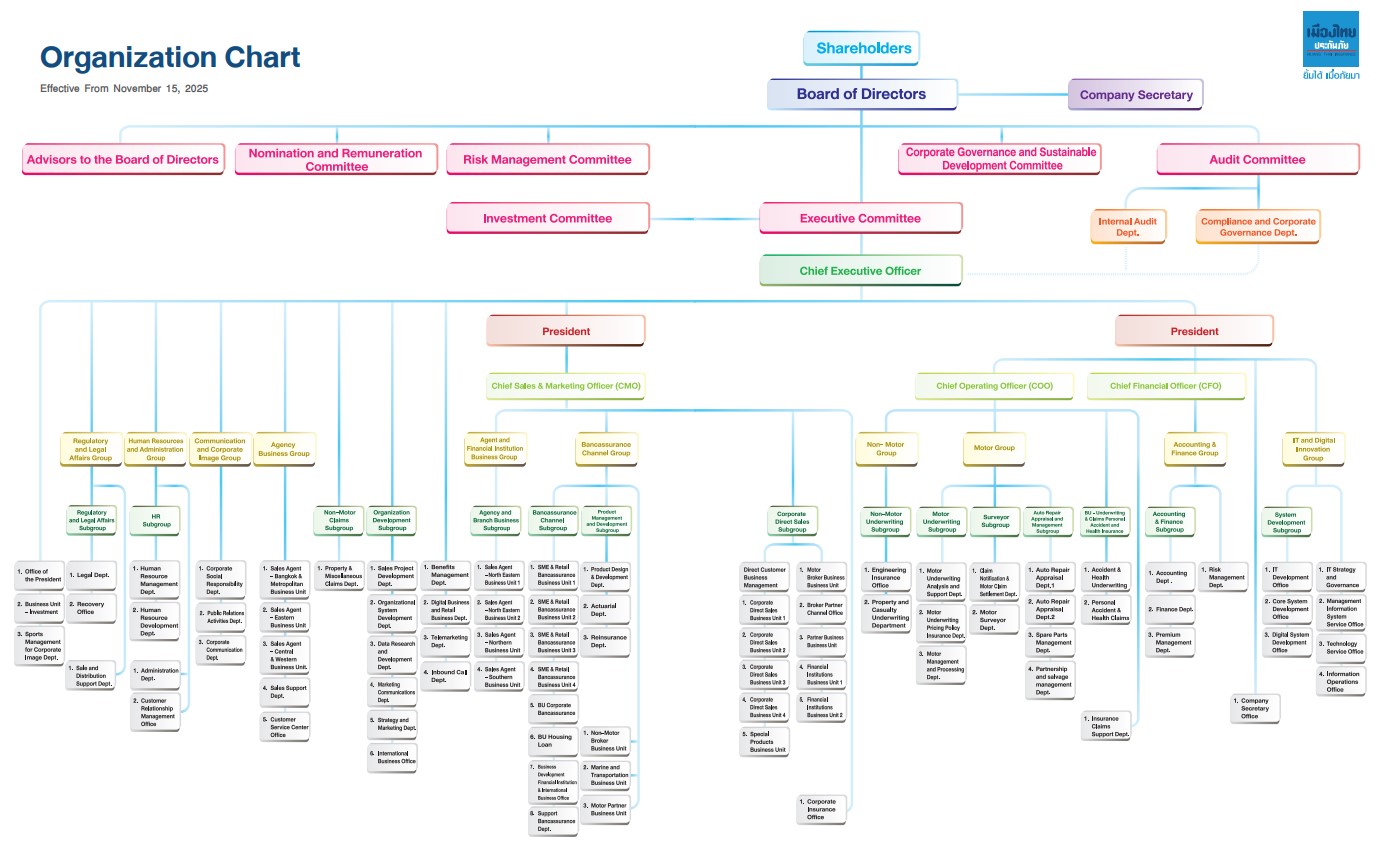
Corporate Governance Policy
Corporate Governance Policy
Muang Thai Insurance Public Company Limited
This policy was approved by the Board of Directors’ Meeting No.1/2026 held on February 27, 2026.
Muang Thai Insurance Public Company Limited has recognized the importance and has always conducted its business with corporate governance. It aims to build confidence for shareholders, customers, investors, employees, suppliers, and all stakeholders by aiming to manage the business effectively, transparently, and fairly with social and environmental responsibility. Also, the Company aims to generate stable financial performance and sustainably grow in long term.
The Company applies Corporate Governance Code for listed companies (CG Code) as specified by the Securities and Exchange Commission and the Stock Exchange of Thailand, the Notification on Good Corporate Governance of Non-Life Insurance Companies issued by the Office of Insurance Commission, and relevant ESG Criteria into the framework to enhance the management towards sustainability.
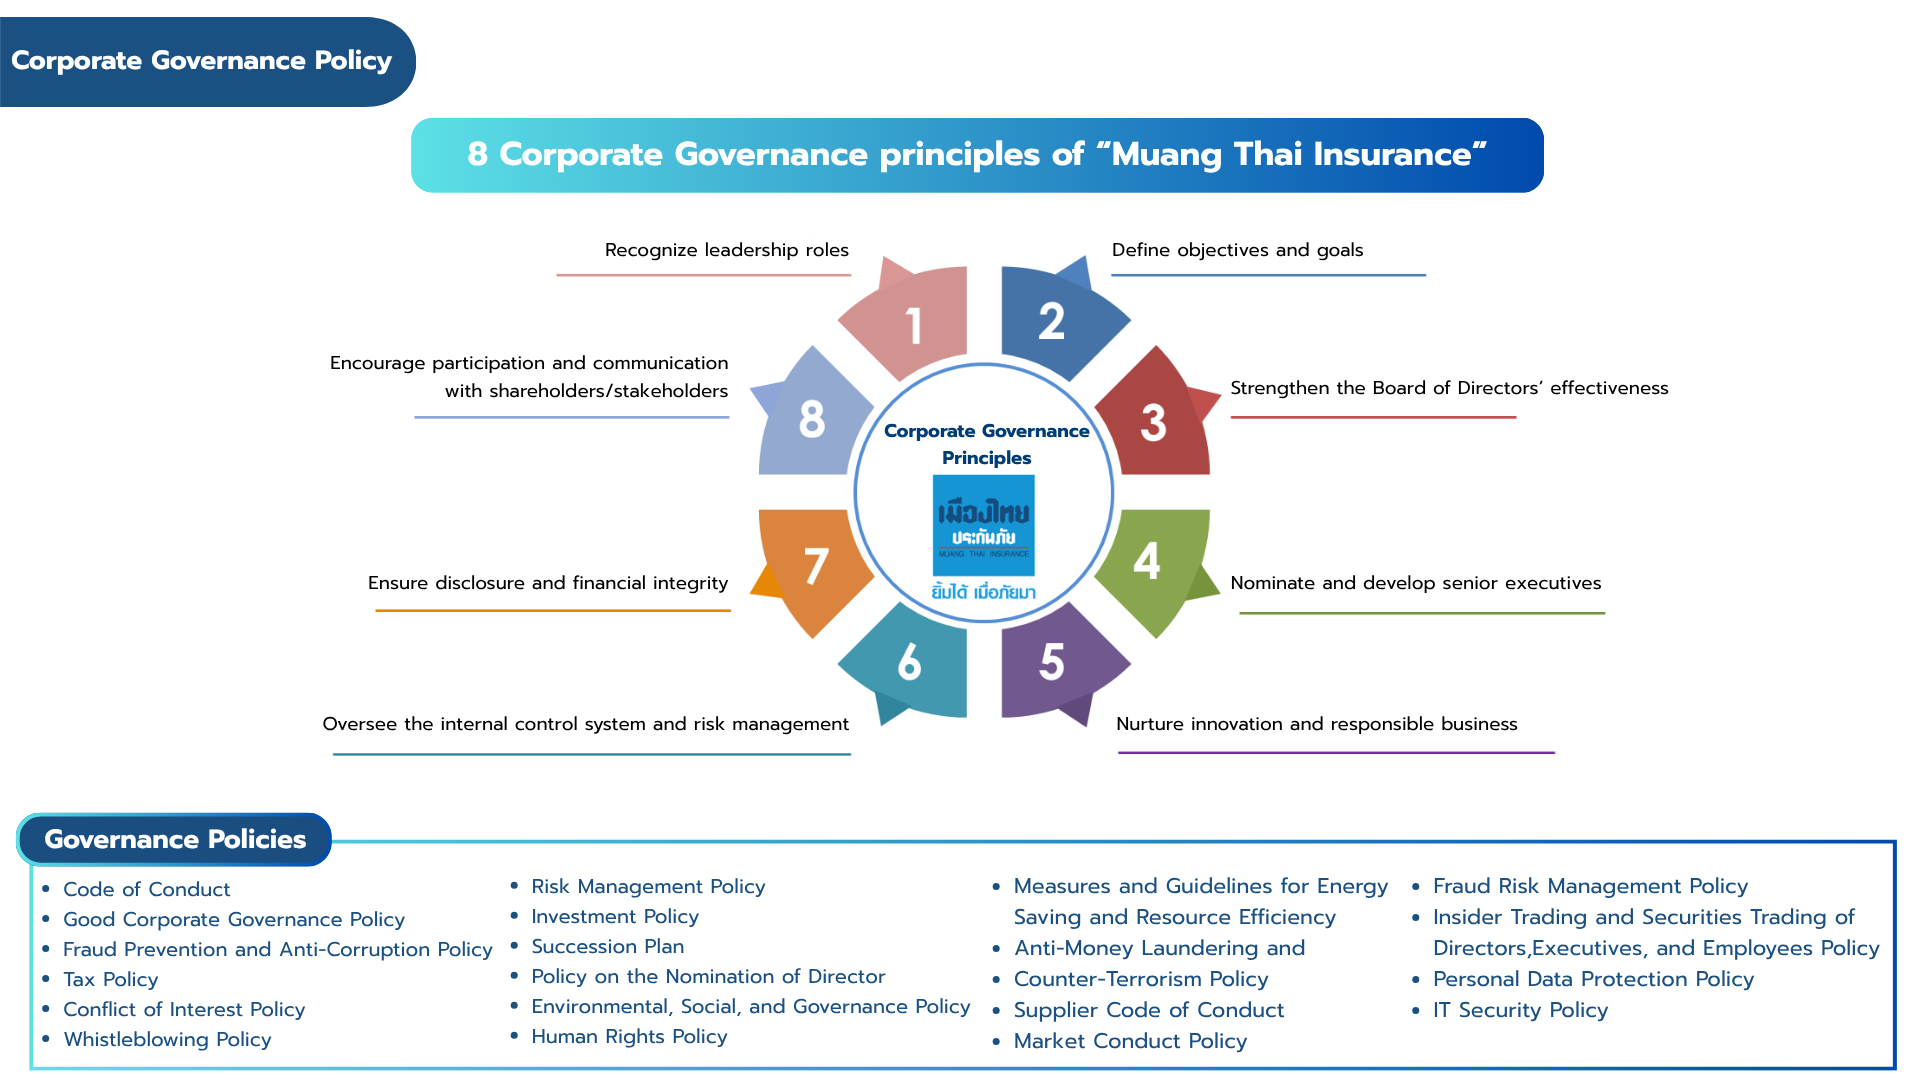
Corporate Governance Principles
1. Recognize the leadership roles and responsibilities of the Board of Directors to sustainably create values for the Company
The Board of Directors performs the duties with responsibility, honesty, and prudence. The Board of Directors determine the direction, strategy, goals, and important policies, as well as supervise the business operation in compliance with laws, ethics, and governance principles to sustainably create values for all stakeholders.
2. Define objectives and goals for sustainable business
The Company defines vision and business goals that prioritize economic growth in line with social and environmental responsibility and governance principles by using technology and innovation to create value for customers, shareholders, and all stakeholders.
3. Strengthen the Board of Directors’ effectiveness
The Company place the importance on the qualification, knowledge, ability, diverse experience, and independence of the directors. The nomination is conducted with transparency. There are performance evaluation and knowledge training for directors continually.
4. Nominate and develop senior executives and employees
The Company determines the nomination guidelines, development plan, and succession plan for executives and employees to drive the organization. Moreover, the Company has the appropriate and fair evaluation system and remuneration.
5. Nurture innovation and responsible business
The Company supports the development of innovation, technology, and products that meet the needs of customers. The Company operates the business with the respect for Human Rights and the responsibility for society, environment, customers, suppliers, shareholders, and all stakeholders under ESG principles and Anti-Corruption.
6. Strengthen effective risk management and internal control
The Company establishes the effective risk management system, internal control, audits, corporate governance, legal compliance, as well as the prevention measures on conflict of interest, fraud, and corruption.
7. Ensure financial integrity and disclosure
The Company places the importance on accurate, complete, transparent, and timely disclosure of financial and other material information, including the fair communication and disclosure to shareholders, investors, and stakeholders.
8. Encourage participation and communication with shareholders
The Company respects and protects the Shareholders’ rights, promotes the participation in decision-making, convenes the transparent and fair Shareholders’ meeting, and facilitates the shareholders to exercise their rights.
บริษัทมีการกำหนดนโยบายและแนวปฏิบัติด้านการต่อต้านทุจริตและคอร์รัปชัน
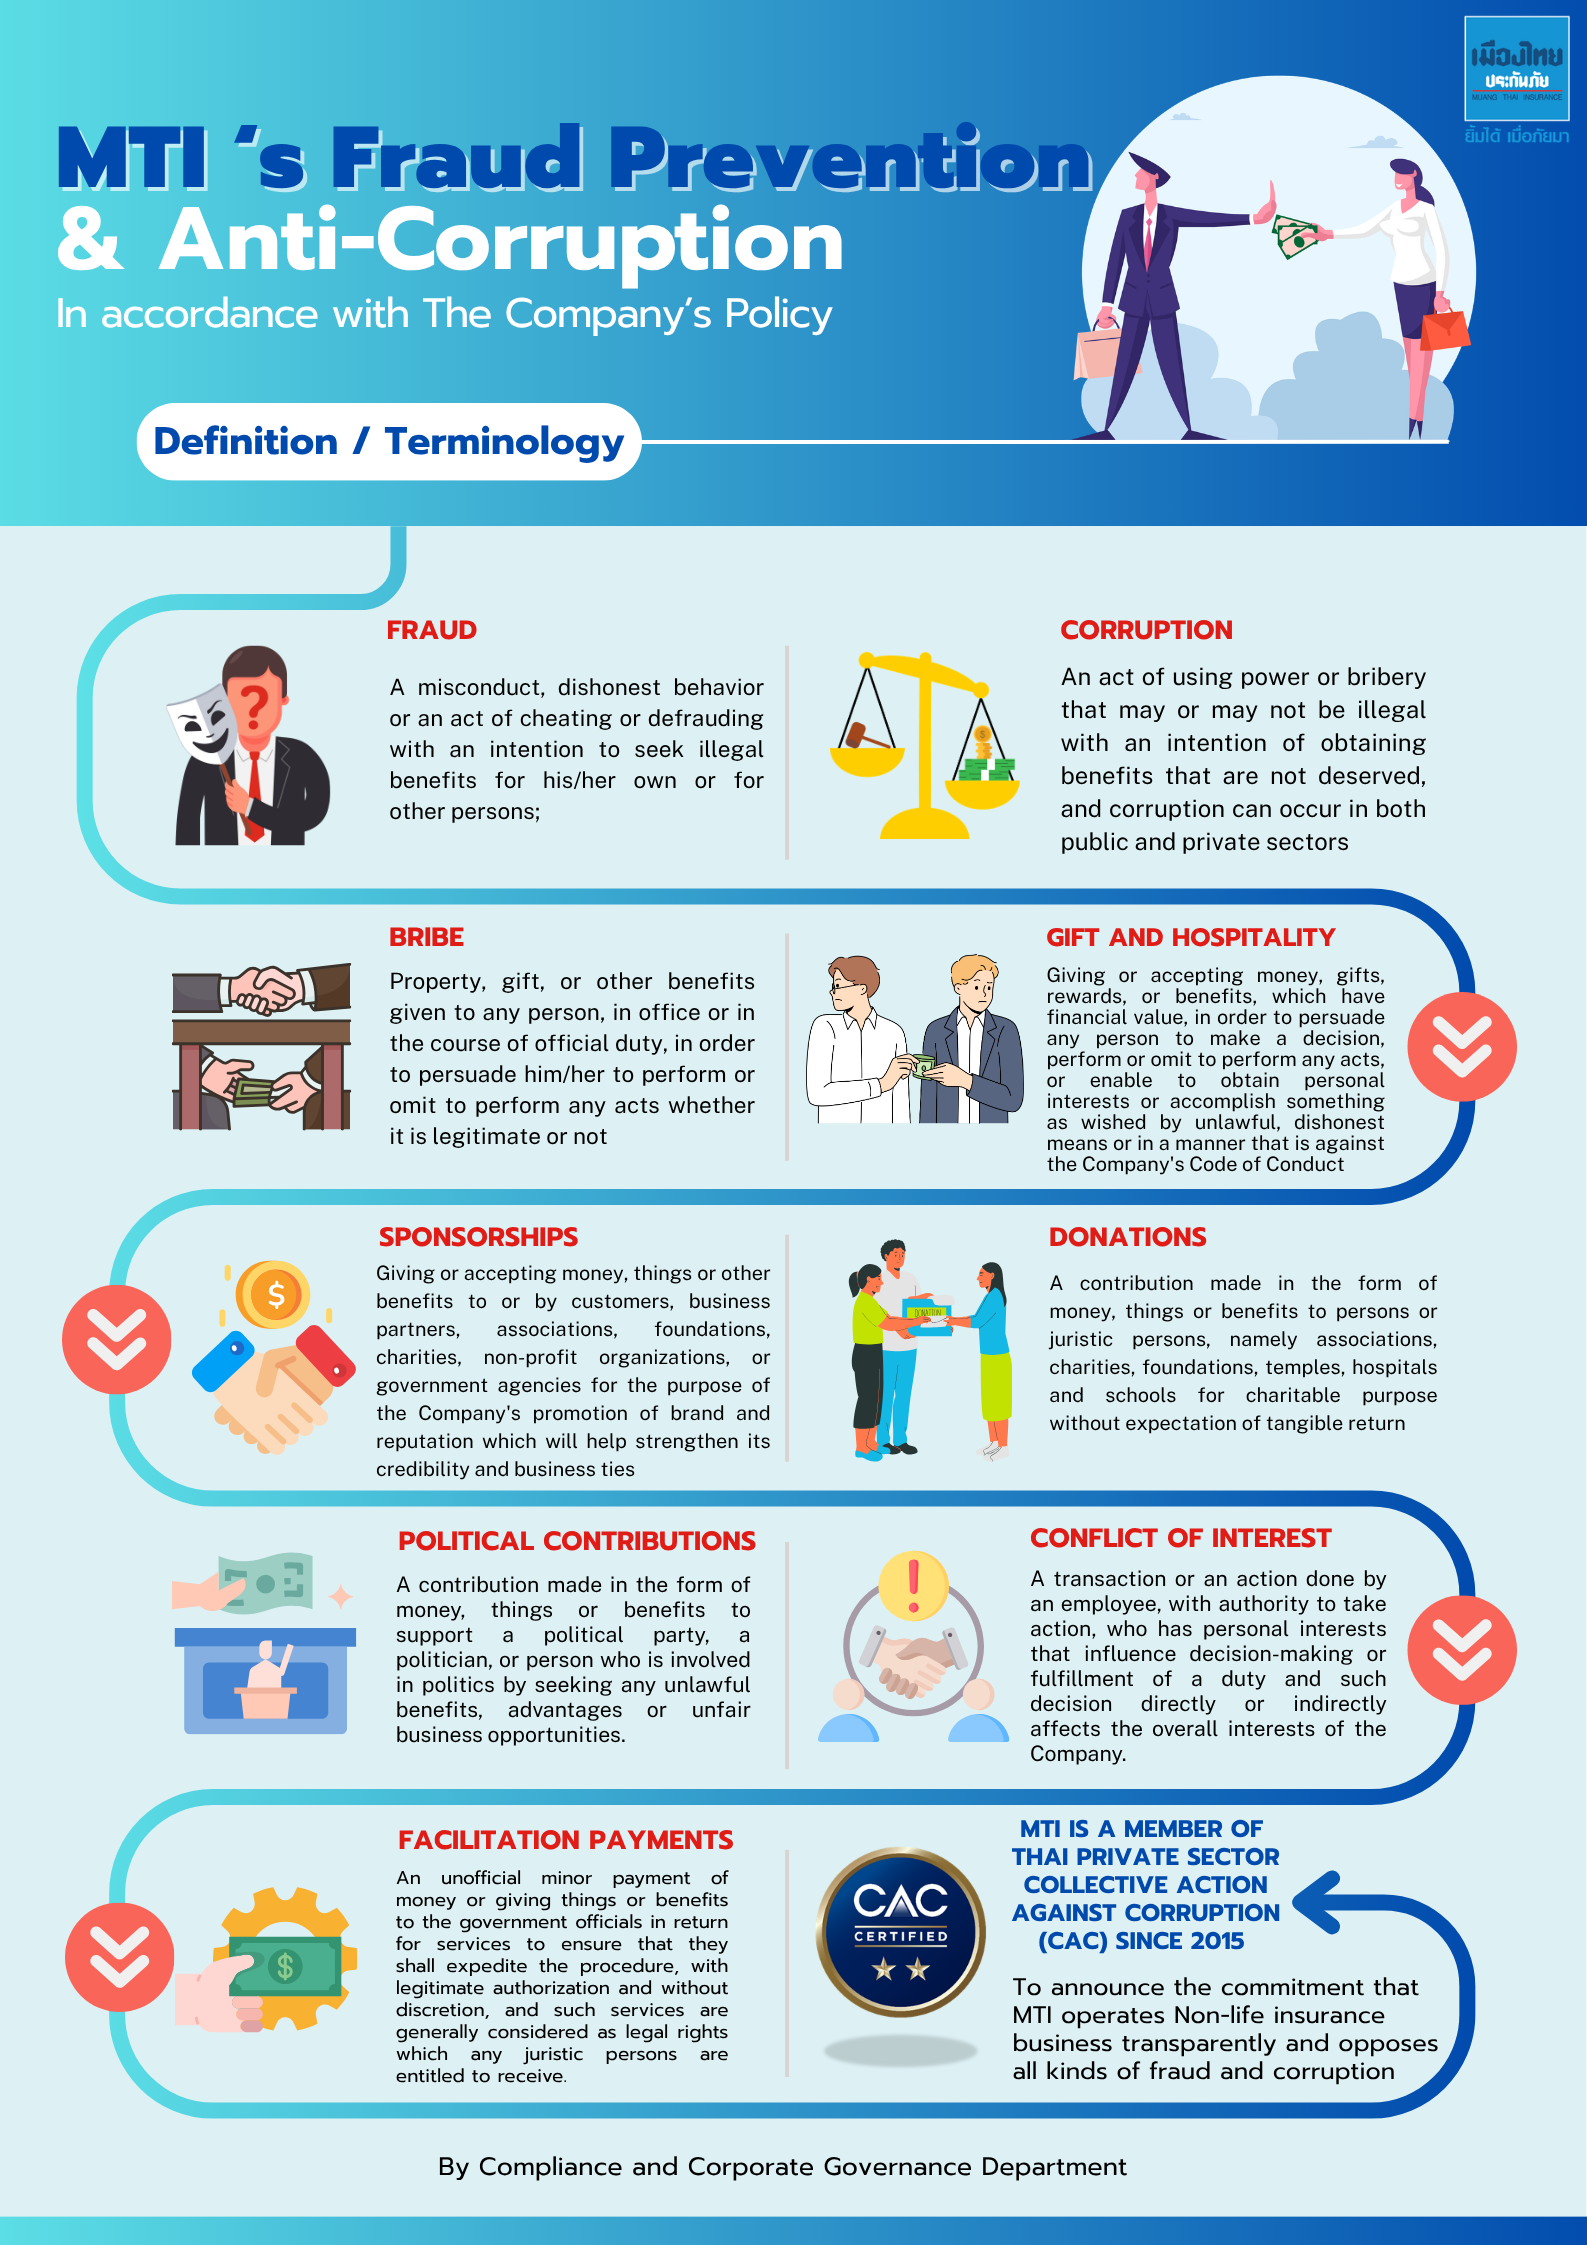
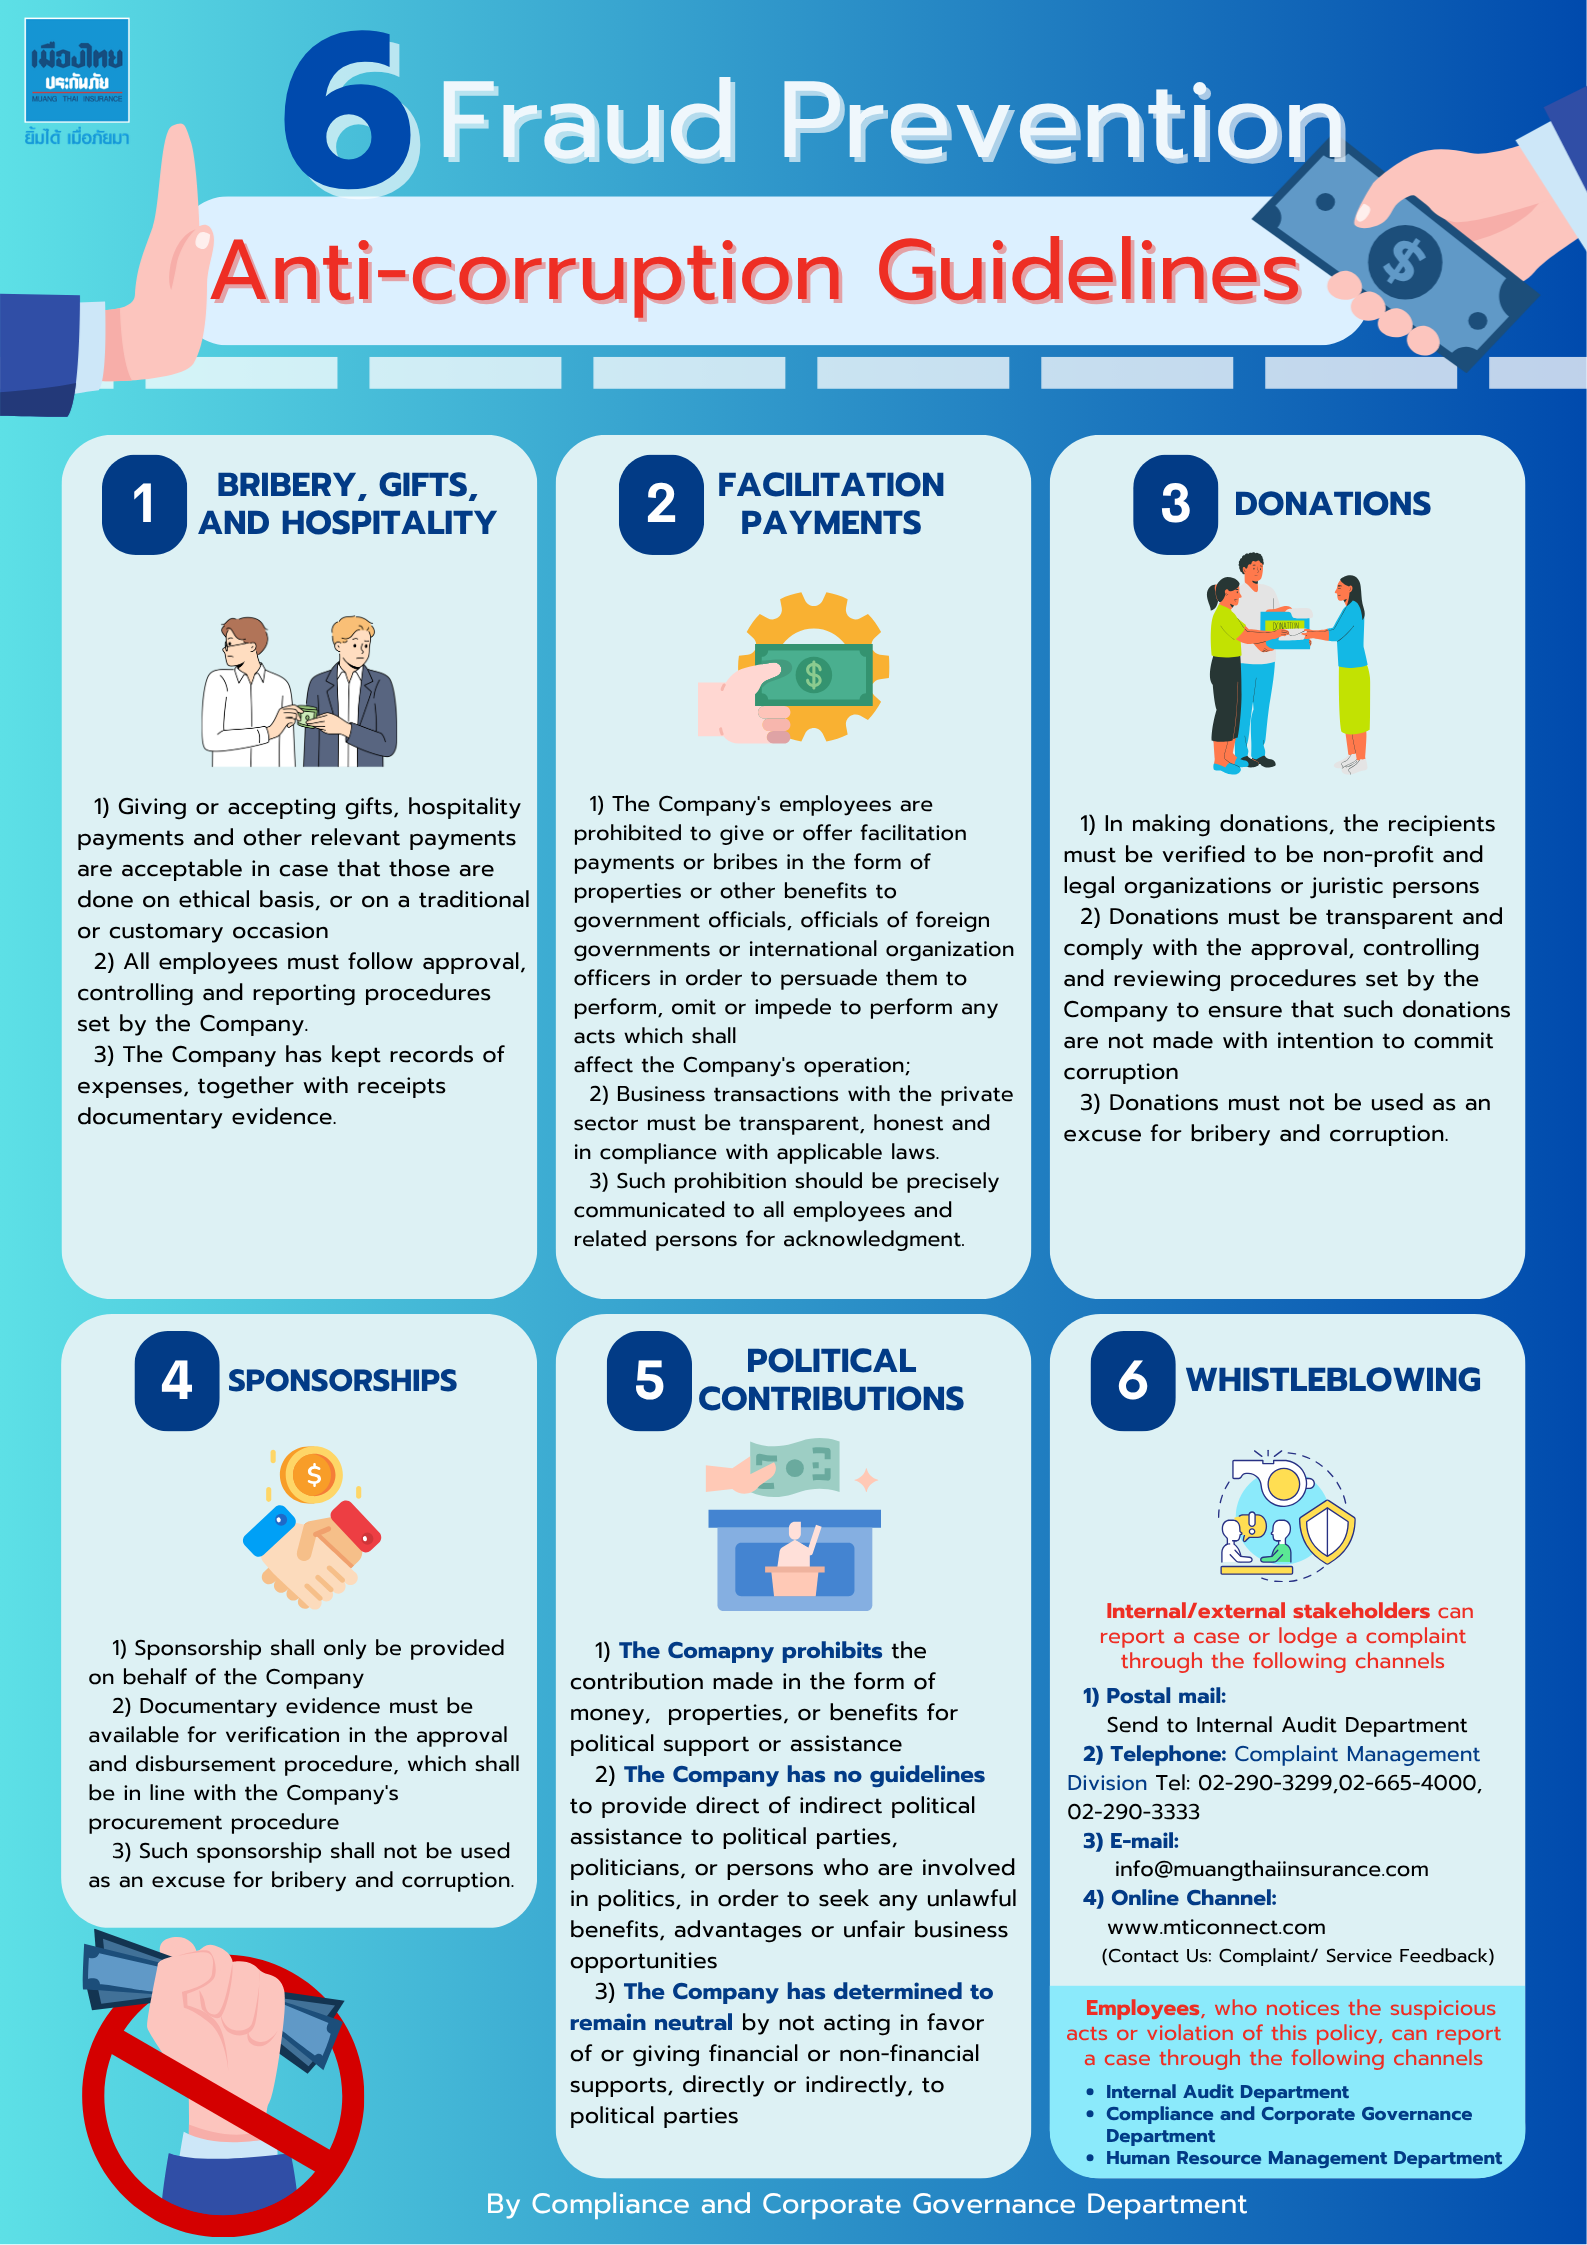
Muang Thai Insurance place the importance on anti-corruption as stated in Fraud Prevention and Anti-Corruption Policy and Guidelines. All executives and employees have duties to comply with the laws, Code of Conduct, rules and regulations related to fraud prevention and anti-corruption. Moreover, they must perform their tasks with transparency by prohibiting any acts related to fraud, corruption, bribery, gifts, property, or other benefits to relevant stakeholders. This includes bribery for seeking business benefits or any acts that are at risk of fraud and corruption.
Moreover, the Company establishes the assessment mechanism and risk management regarding fraud prevention and anti-corruption, control and governance measures to protect and monitor risks under the risk appetite, oversight and evaluation measures, and fraud prevention and anti-corruption guidelines.
MTI is certified as a member of Thai Private Sector Collective Action Against Corruption (CAC)
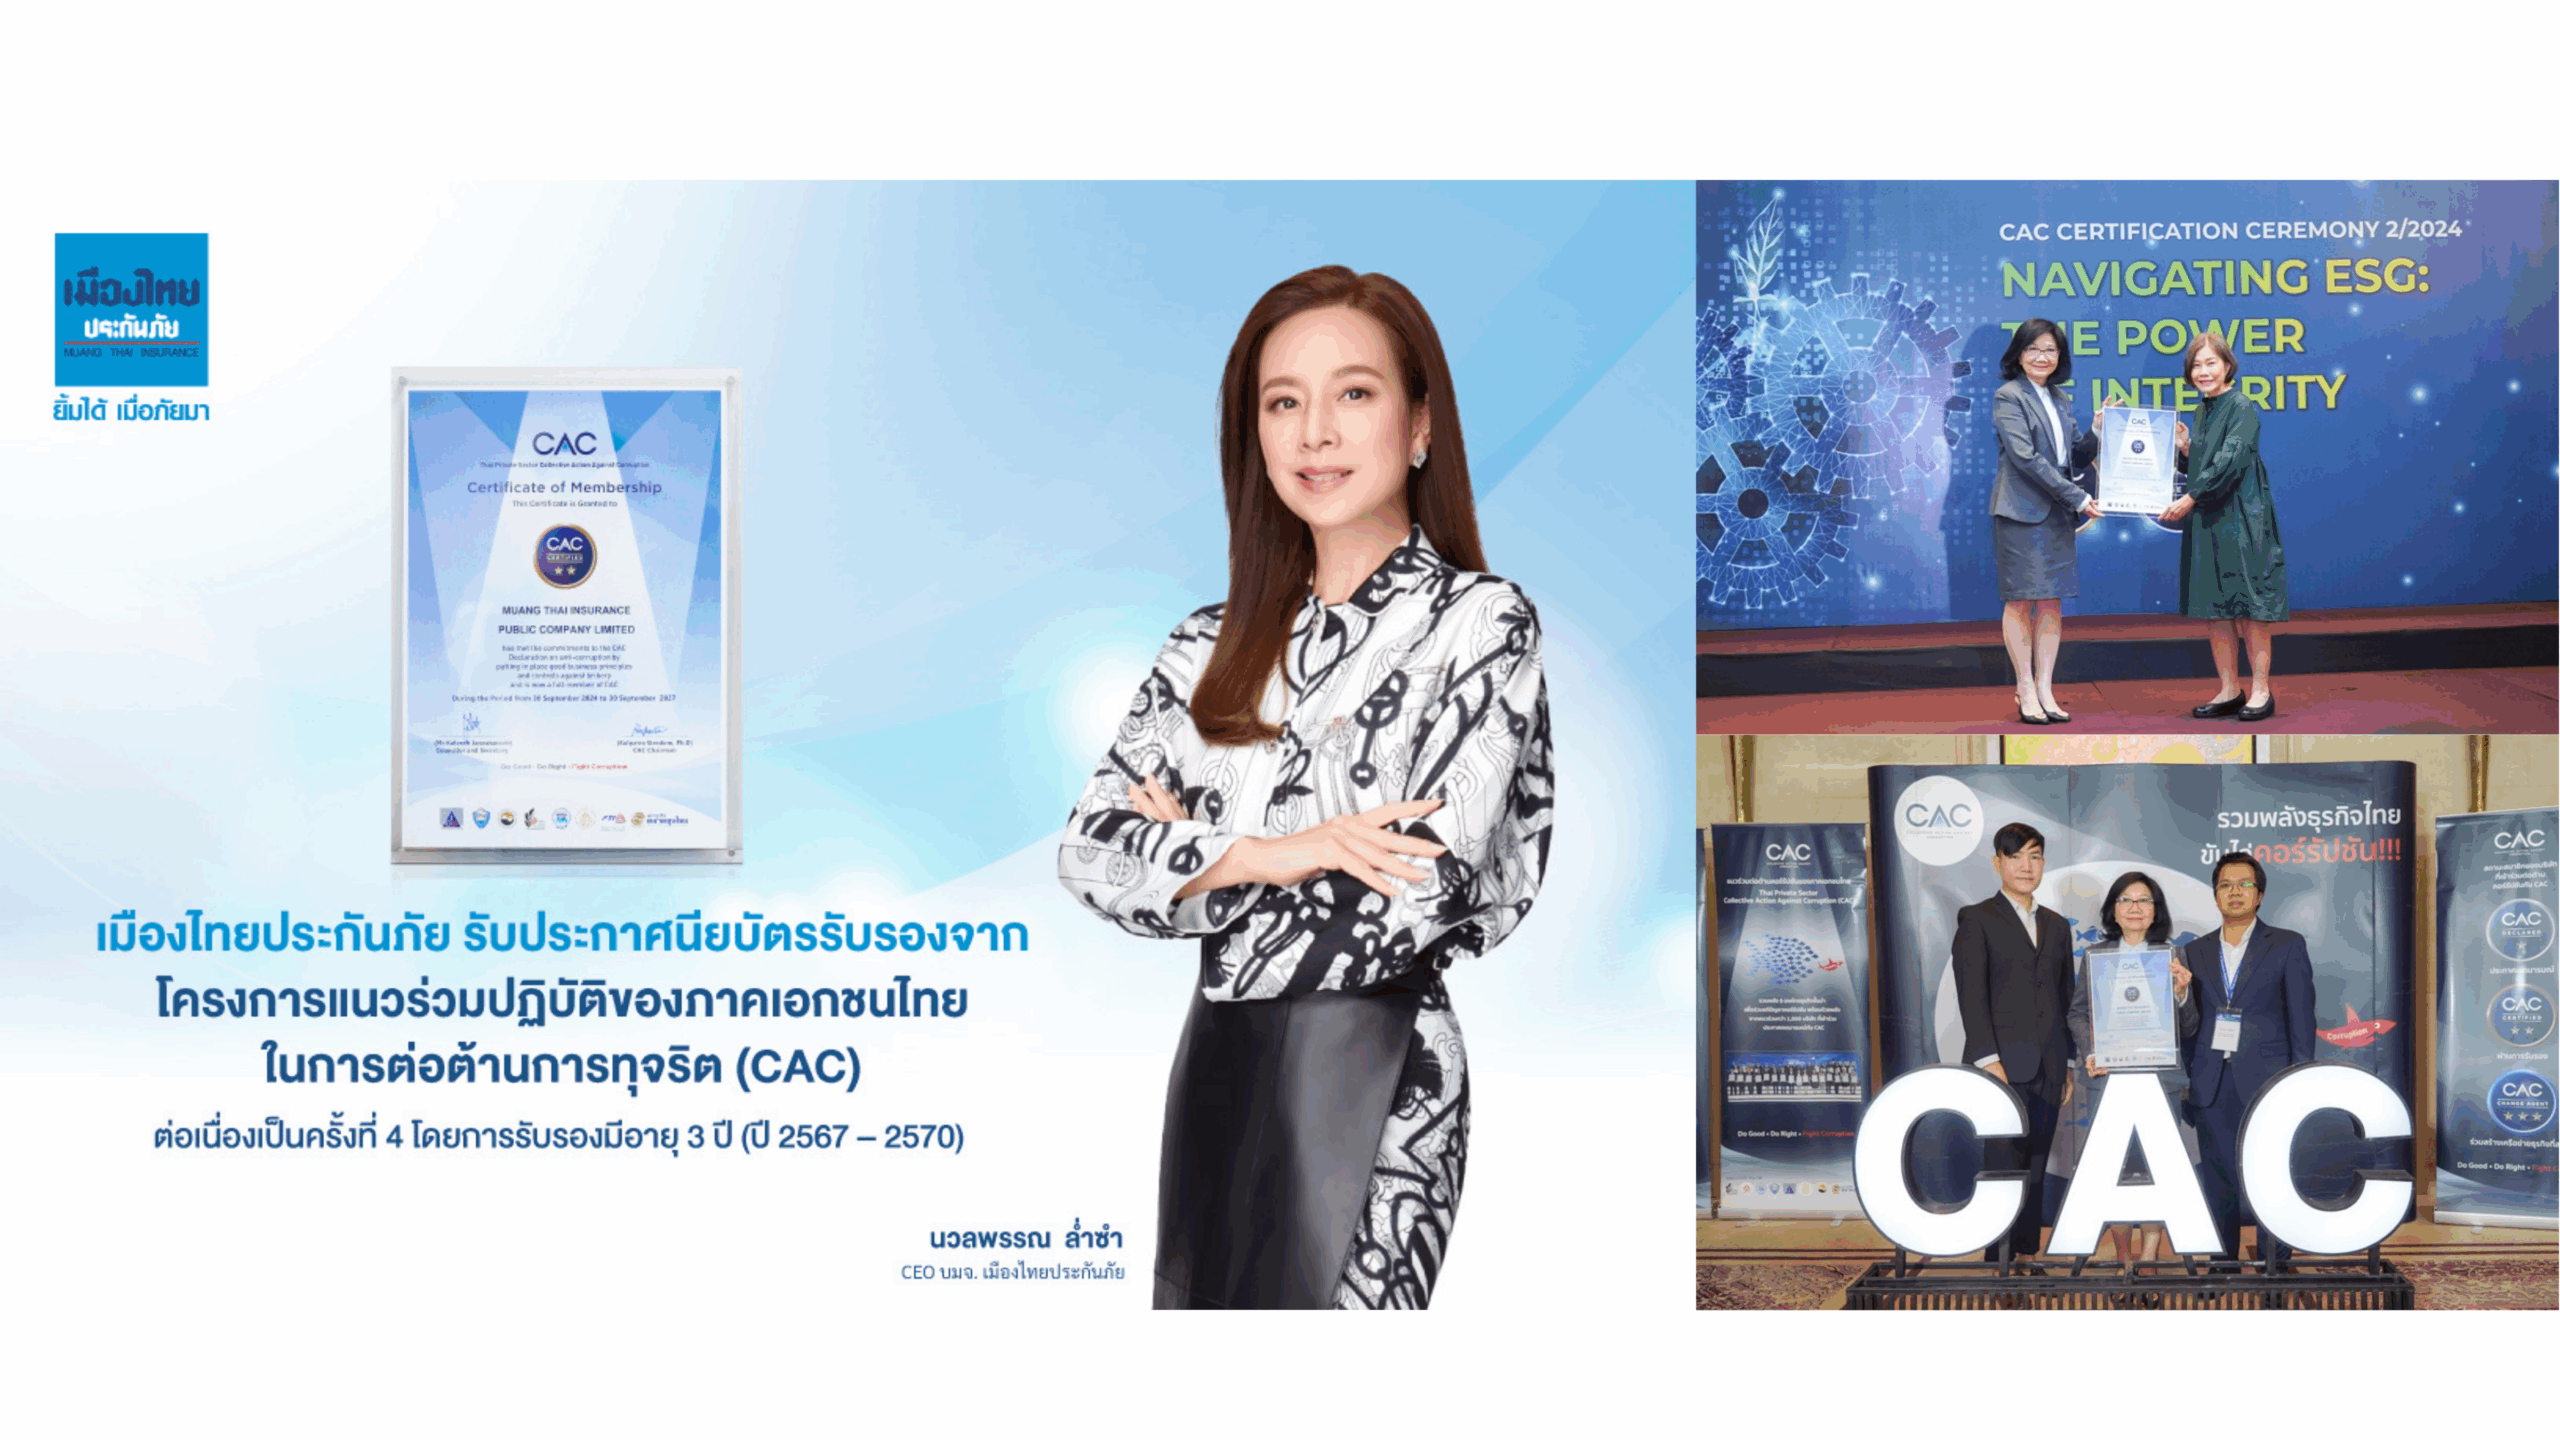
Muang Thai Insurance Public Company Limited has been certified as a member of the Thai Private Sector Collective Action Against Corruption (CAC) in 2024 from Thai Institute of Directors (IOD) for the fourth time (the third renewal in 2024) since 2015. The certification is valid for 3 years from 2024 to 2027
Muang Thai Insurance adheres to honesty under governance principles. We aim to develop the organization in line with the fraud prevention and anti-corruption, especially transparent work with internal and external parties including employees, customers, suppliers, business partners, and agents.
Digital Transformation & Innovation
Muang Thai Insurance Public Company Limited are aware of the changes in digital technology, consumer behaviors, and competition in non-life insurance industry. Hence, digital and innovation development becomes one of significant factors that affects the competitiveness, work efficiency, and customer experience in long term. As a result, the Company determines digital transformation and innovation as a part of corporate strategy to enhance business potential, risk management, and product and service development in order to meet the needs of the customers effectively and prepare for timely changes in the future.
Digital development of the Company aims to utilize technology and information to support the operation across value chain, consisting of the sales, underwriting, policy management, claim management, payment, customer stewardship, and data management. The Company cultivates the data-driven organization and innovation-driven organization to increase the effectiveness, reduce complexity, and sustainably create unique competitiveness.
The Company Aims to Develop the Organization to
Digital-driven Insurance Company
The organization that use data, technology, and innovation as value creation mechanism for customers to enhance work efficiency and support effective decision-making under corporate governance principles, data security, and responsibility towards all groups of stakeholders.
1. Digital Customer Experience
| Enhancing customer experience and the access to insurance services through convenient, fast, and easy digital platforms and self service Key Initiatives
|
2. Data-driven Organization
| Promoting the use of data for decision-making to increase efficiency in risk analysis, product development, and service development Key Initiatives
|
3. Automation & Artificial Intelligence
| Utilizing AI technology and automation integrating in main operation to improve effectiveness, reduce time consumption, and enhance service quality Integration
|
4. Operational Excellence
| Using technology to enhance operational efficiency Key Initiatives
|
5. Sustainable Innovation
| Developing innovation that support the sustainable goals Example
|
Target | Indicator | Performance in 2025 |
Enhancing the access and customer experience through digital channels | The number of website users | 2,282,949 users |
The installs of Application Muang Thai Friends | 77,535 times | |
The amount of E-policy | 319,771 policies | |
Increasing the work efficiency through Automation and AI | Testing AI Vehicle Inspection for Self-service underwriting | Implemented |
Data-driven Organization | Developing Customer Data Management | Under implementation |
Using data and customer feedback to develop products and services | Under implementation | |
Enhancing the data partnership with business partners | Developing API Integration for suppliers and brokers | Implemented |
Developing employees’ digital and innovation skills | AI Familiarization for MTI’s Management | Implemented |
AI Training & Workshop | Implemented | |
Digital Learning Platform: MTI Learn D | Implemented | |
Supporting the paperless operation | Reducing paper usage through E-policy and Digital Workflow | Under implementation |
Core Initiatives
The Development of Digital Channel for Customers
Muang Thai Friends
Customers can experience the following:
- Checking policy’s information
- Checking coverage
- Searching service networks
- Claim notification
- Receiving privileges and benefits for 24 hours
E-policy Development
The use of AI in Non-life insurance
The Company adopts the use of AI to support the main business operation such as
- AI Vehicle Inspection: Testing AI Vehicle Inspection for Self-service underwriting to improve the accuracy, reduce time, and enhance customer experience.
- Claims Monitoring: Using for following claim status and notifying a delay in claim process. This can reduce errors and boost the efficiency of relevant departments.
Data Partnership
Digital Skills Development
By having programs as follows:
- MTI LearnD
- AI Familiarization for MTI’s Management
- AI Training & Workshop
- Digital Skills Program
- Digital Mindset Development
In 2025, executives and employees were trained and improved digital skills, including AI technology, Data Analytics, Digital toolkits, and Cyber Security to enhance work efficiency and prepare for the future technology.
Future Initiatives
- Single Customer View
- Advanced Data Analytics
- AI & Responsible AI
- Digital Ecosystem
- Intelligent Automation
- Customer Experience Innovation
- Sustainable Insurance Innovation
Data Protection & Cyber security
Importance
Customer data and internal data are the most valuable property for the Company. Damage, Cyber attack, or personal data breach might impact the business in terms of reputation, customer trust, costs, and legal risk under the business context of digital era. Cyber Security is not only “the risk protection” but also “important opportunity” to sustainably build the trust and competitive advantage.
TARGET
Maintaining cyber security according to international standard and Personal Data Protection Act (PDPA) 100%
No incident of cyber attack and data breach
Promoting the culture of Cybersecurity Awareness among employees at all levels
Developing internal control system and conducting cyber drill across all departments
Personal Data Protection Policy
Muang Thai Insurance Public Company Limited recognizes the importance of the protection of customers, insured, service providers, employees, suppliers, and stakeholders’ data. Therefore, the Company establishes the Personal Data Protection Policy to be a governance framework for collecting, using, disclosing, and transferring personal data according to the Personal Data Protection Act B.E. 2562, relevant laws, and international personal data protection standards in order to ensure that the personal data are protected appropriately and securely, and the rights of data subjects are respected.
Objectives
The Company formulated this policy to be criteria for managing personal data management, covering collecting, using, disclosing, and transferring personal data. Moreover, Data Security Measures are formulated, and the protection of personal data owner’s rights according to the relevant laws.
Scope
This Policy applies to the data subjects who make transactions or have business relationship with the Company such as customers, insured, claimants, beneficiaries, suppliers, contractors, directors, employees, applicants, website visitors, application users, others service channels, and external parties who use personal data on behalf of the Company.
Personal Data Protection Principles
The Company has procedures regarding personal data according to the following principles.
1. Purposes of Collection, Use and Disclosure of Personal Data
The Company shall collect, use, and disclose personal data as necessary for lawful purposes, transparency, and fairness by complying with the legal standard as appropriate and notifying the data subject for consent as required the laws.
2. The Use of Personal Data in accordance with specified purposes
The Company shall use the personal data only according to the purposes prior notified to the data subjects and shall not use the data for other purposes, except the data subjects give the additional consent or the compliance with a legal obligation.
3. The Collection of Personal Data as necessary
The Company will collect the personal data as necessary for service, contract obligation, legal obligation, underwriting, policy management, claim payment, and related business operation.
4. Accurate and up-to-date data
The Company shall ensure that the personal data is accurate, complete, up-to-date, and not misleading to support the effective service.
5. Data Protection and Security
The Company establishes the appropriate technical and corporate measures to protect the loss, access, use, change, or disclose the personal data without consent. Moreover, the Company continuously review the security measure on regular basis.
6. The limitation of retention period.
The Company shall retain the personal data for processing the data in the necessary period or as required by the laws. When the period is expired, the Company shall erase, destroy, and anonymize the personal data which cannot identify the data subject.
The Rights of data subjects
The Company respects the rights of data subject as specified by the laws, including
- The Rights to withdraw consent
- The Rights to access and obtain a copy of personal data
- The Rights to amend the personal data to remains accurate and up-to-date
- The Rights to object the data processing
- The Rights to erase or destroy personal data
- The Rights to restrict the use of personal data
- The Rights to transfer personal data as required by the laws
The exercise of the following rights shall be in accordance with conditions and exclusion as specified by the laws.
The Disclosure and Transfer of Personal Data
The Company may disclose the personal data to the regulators, contractors, service providers, or external parties related to the business operation under Privacy Principles and Personal Data Protection Measures, as well as transfer data to foreign countries according to regulations and conditions as specified by the laws.
The Use of Service from data processors or external parties
The Company might use the service from external parties to support the business operation by selecting the service providers who have appropriate personal data protection standard. Also, there are contracts and agreements that specify the clear roles and protection measures.
The Violation of Personal Data
In case of the violation of personal data, the Company shall audit and assess the case and notify the regulators and the data subject for acknowledgement according to the regulations and within the specified period as required by the laws. Moreover, the Company shall implement the remediation and prevention measures.
Oversight and Compliant
The Company has appointed the Data Protection Officer (DPO) and established the complaint procedures regarding the personal data protection for acknowledgement, audit, and appropriate and fair remediation.
Policy Review
The Company may review, develop, or revise the Personal Data Protection Policy in line with the business operation, technological changes, and legal requirement by publishing the current policy on the Communication channels allowing the related persons to access conveniently.
This policy was reviewed and approved by the Board of Directors’ Meeting No. 4/2024 held on November 13, 2024.
The effective date was November 13, 2024 onwards.
Implementation
The Company implements the holistic cyber security and personal data protection by integrating technical measures and process and promoting awareness among employees, as follows:
1. Cyber security Management
The Company systematically implements the cyber security management measures according to the international standards by reviewing and revising Data Security Policy on regular basis to align with the new threats. The Company will use the technology and security process such as Cyber Threat Protection, Data Encryption, Access Control, Vulnerability Assessment & Risk Management, and Penetration Test to monitor, audit, and proactively reduce risks. The Company has formulated the Incident Response and Recovery Plan to handle the emergency incident by conducting Cyber Drill once a year to improve the readiness of employees and work process in order to tackle the threats effectively.
In terms of employee development, the Company places an importance on promoting the culture of Cyber Security Awareness through training on annual basis. In 2025, there were 4 online and on-site training, covering risky group 280 persons. All employees must pass the Cyber Security test. Furthermore, the Company set the target to protect cyber threats 100% to secure the data and maintain the confidence of stakeholders sustainably.
2. Personal Data Protection
The Company systematically and strictly protects the personal data protection according to Personal Data Protection Act (PDPA) by formulating Privacy Policy and Privacy Notice, covering the objectives, the use, collection, and transparent disclosure. The Company also appoint Data Protection Officer (DPO) who is responsible for overseeing, monitoring, and providing consultation to departments to ensure the use of data aligning with international laws and standards.
The Company controls the access to data through self-verification and access limitation according to roles. There are data collection and processing measures concerning the necessity and security. Also, the Data Breach Response Plan is formulated to prepare for the future incidents by determining the notification process, containment, and reporting to related stakeholders.
3. Employees Development on Data Security
The Company convenes PDPA and Cyber security Awareness Training for new and current employees on regular basis, at least once a year, to increase personal data protection awareness, reduce human errors, and promote the culture of data security by conducting Cyber Drill, testing resilience, and providing suggestions and accurate guidelines.
Performance
The Company has been managing the data security and IT system effectively since January 2025 by having the following results:
- No data leakage or theft (0 case)
- No complaints regarding personal data from customers or stakeholders
- Data Security System passed the test 100%, covering data encryption, access limitation, and risk assessment
- 100% of employees passed PDPA Compliance Training
- The Company conducted Cyber Drill and Cyber security Awareness training, at least once a year, in line with the target.
- Data encryption and self-verification cover the access to important data.
These results reflect the strength of Cyber Security and Personal Data Protection Measures, which enhance the confidence of customers and society and support the corporate sustainability in long term.
Creative Innovation
The Company cooperates with KBTG Co., Ltd. to innovate InsurTech for car inspection by using Artificial Intelligence (AI), the first of its kind in Thailand, to facilitate the customers via digital platforms. Formerly, the customers shall make an appointment with the Company for the car inspection before underwriting, which consumed time and required high costs.
Corporate Risk & Opportunity
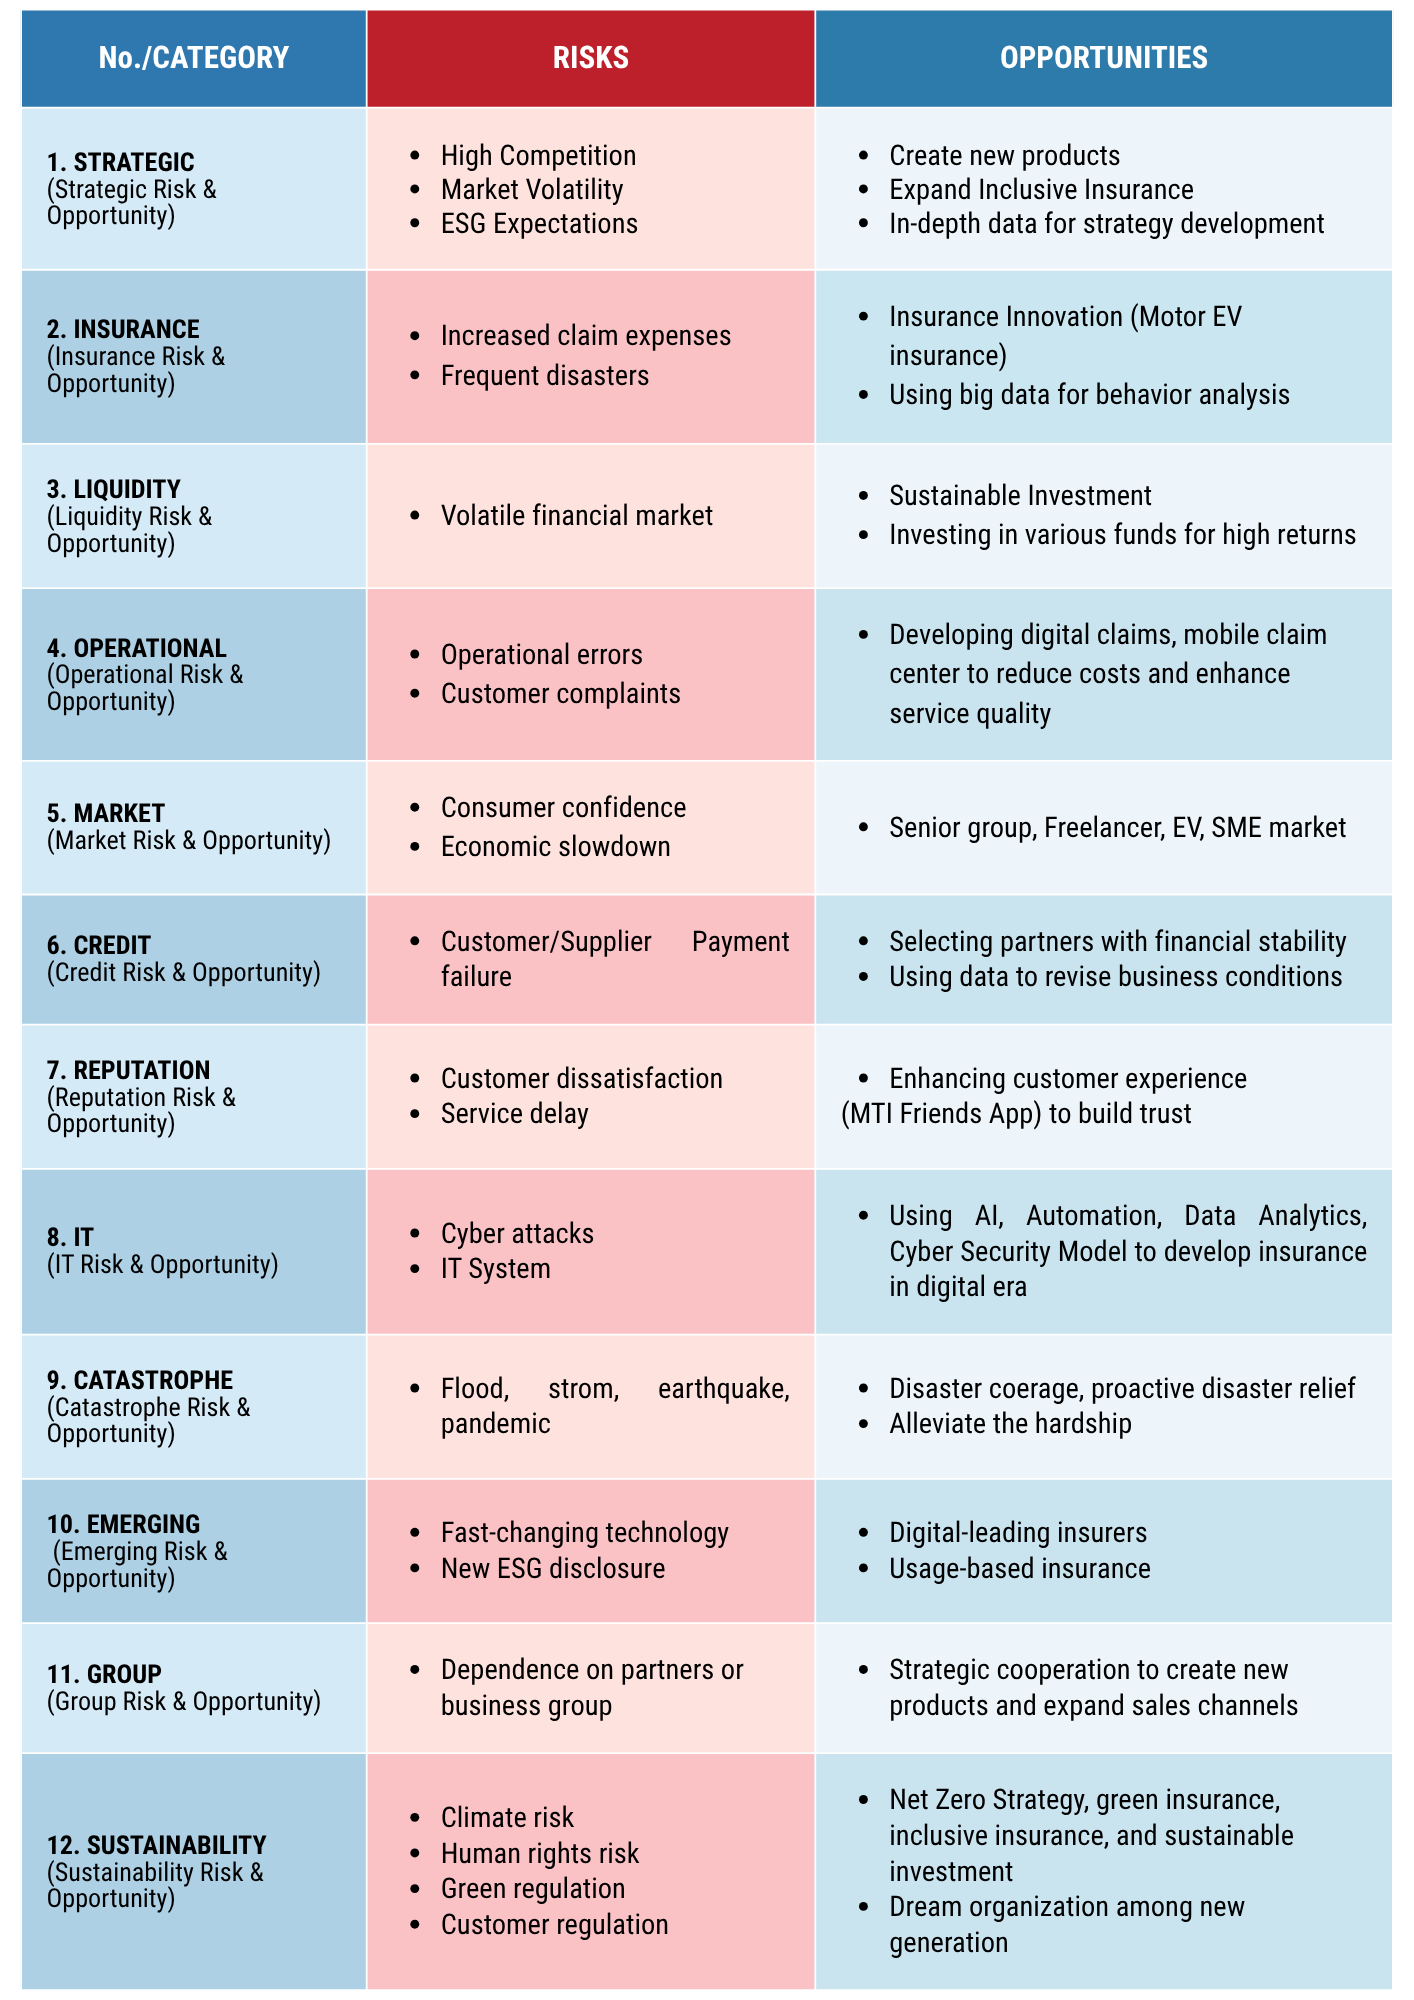
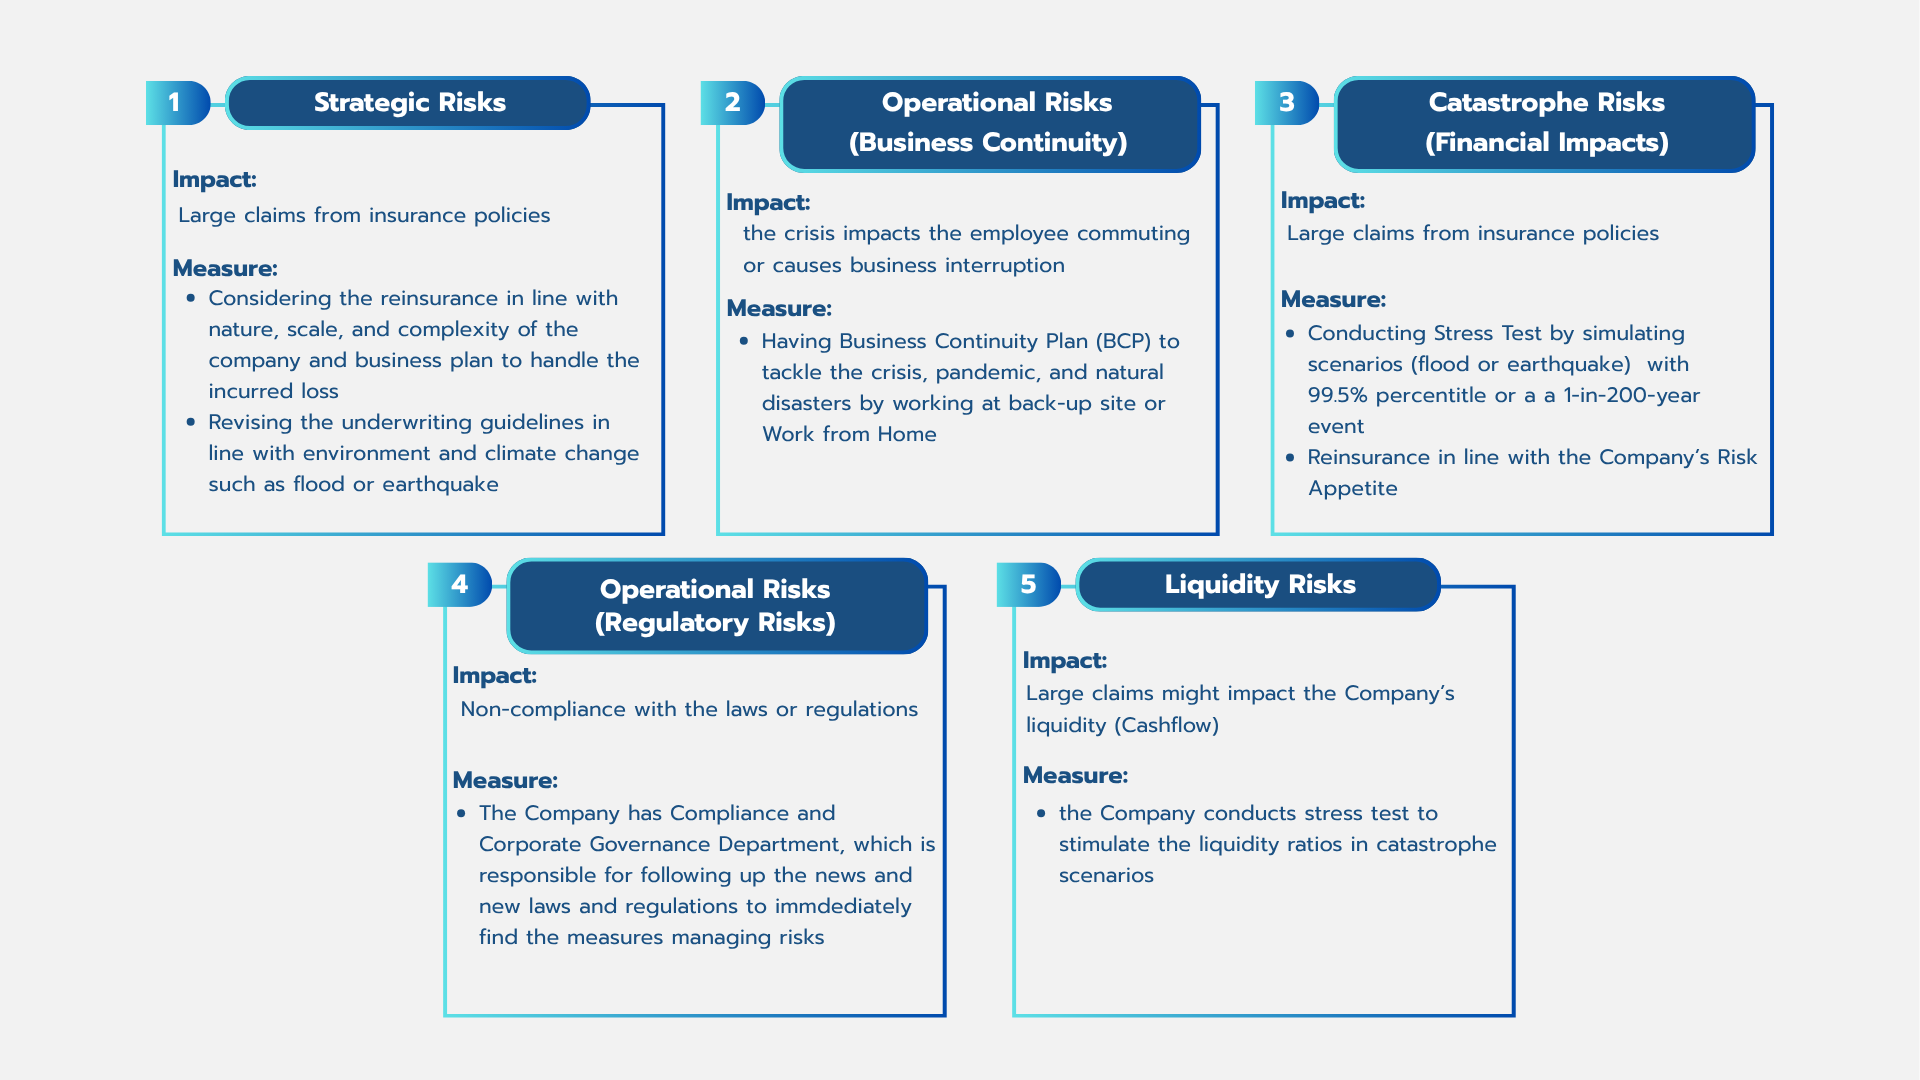
Muang Thai Insurance develops the Risk Management Framework, covering the critical risks and ESG-related risks, by having objectives to support the business operation and the stable, transparent, and effective growth under fast-changing environment in terms of economic, social, technology, and climate.
The Board of Directors and the Risk Management Committee are responsible for ensuring the risk management policy in line with the strategy, vision, and mission. In addition, the criteria, methodology, and conditions of risk and opportunity assessment are determined for systematic management, transparency, impact mitigation, and value creation for business, employees, shareholders, customers, and society.
MTI’s Risk Management System manages the following risks:
- Financial and Insurance Risks
- Strategic, Operational, and Technological Risks
- ESG Risks such as Climate, Human Rights, Diversity, Governance, and Consumers’ expectation
The Company reviews the risks and opportunities on regular basis, determines the preventive plan, reduce impacts, and develops strategic opportunity to increase competitiveness.
Risk & Opportunity Landscape
The Risk Management Strategy and Guidelines
Opportunity Creation from the Risk Assessment Results
The Risk Assessment Results
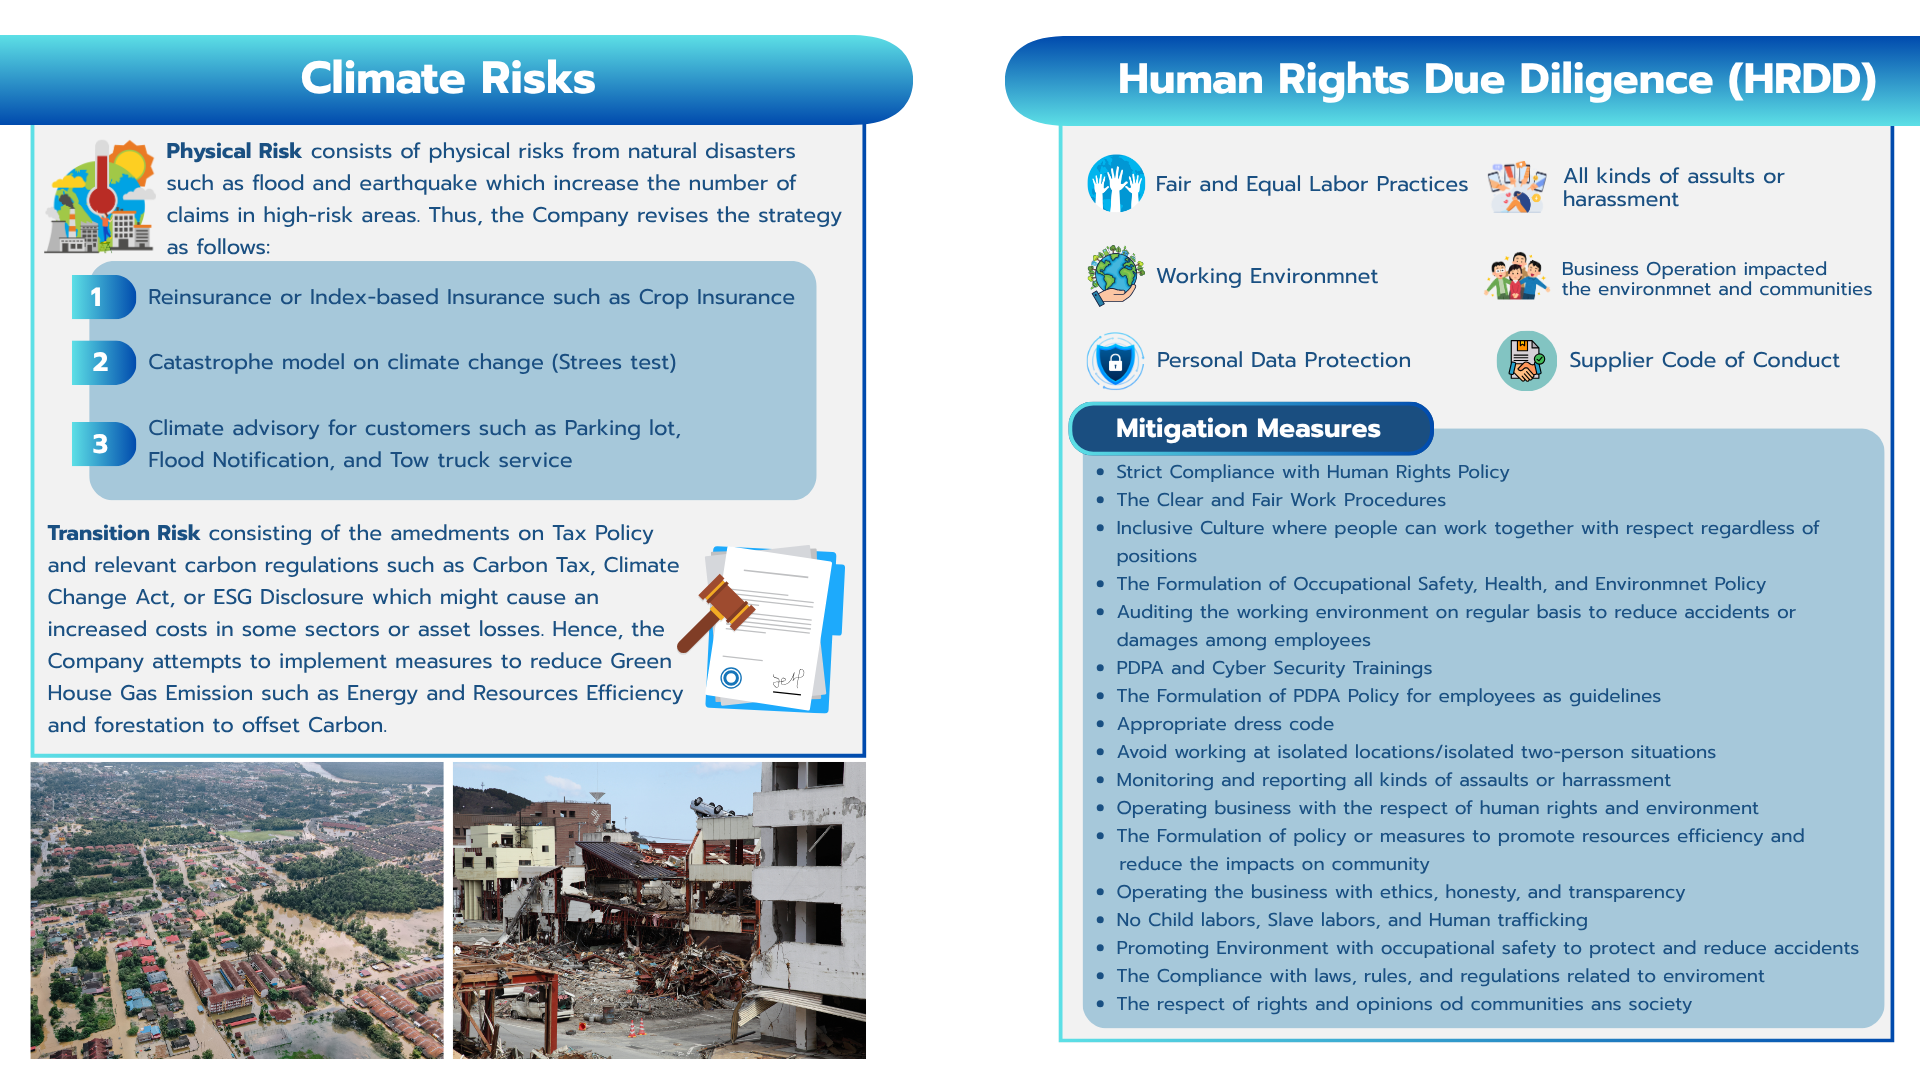
The Climate Risks Management
Good Sales Standard
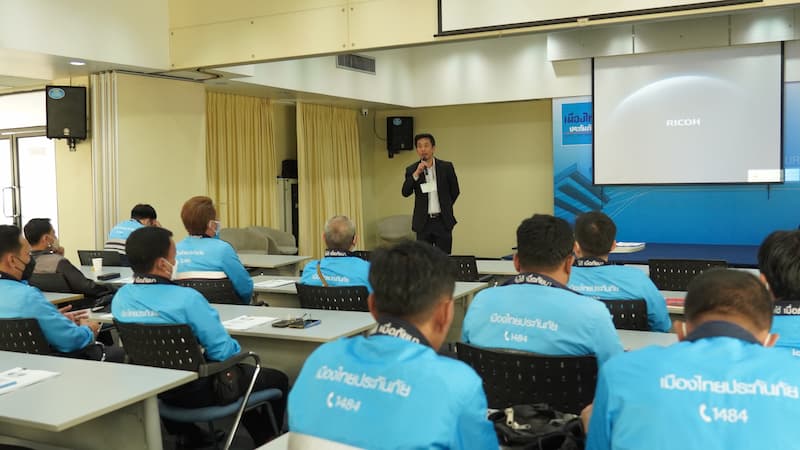
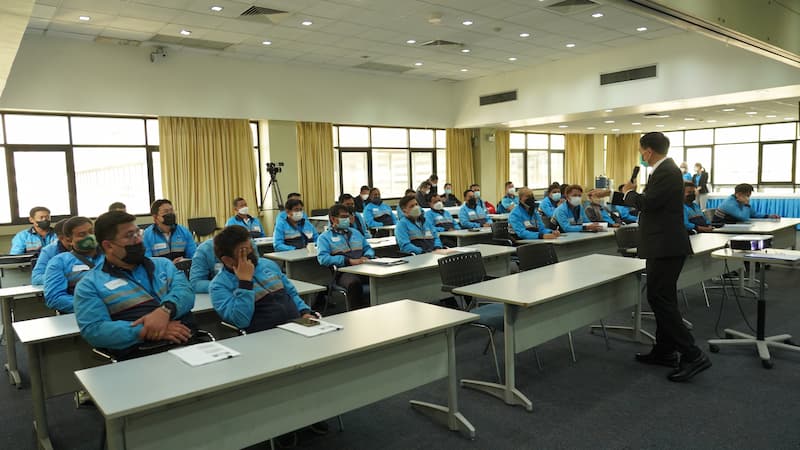
- The Oversight and Development of Agents and Brokers such as agents/brokers who pass the training courses as required by the Company
Insurance Agent and Broker License training for agents and brokers and License Renewal according to courses and conditions specified by the Office of Insurance Commission (OIC), consisting of 8 courses.
The Company introduced a self-learning platform called “Learn Anywhere”. As a result of using Learn Anywhere with License training, the program has shown significant success, with over 13,600 users, and has been continuously updated to ensure it remains modern and comprehensive.
Delivering Exceptional Customer Service
The Company places high importance on customer service and support, ensuring customers can easily report any inconveniences or complaints related to the company’s products or services, allowing for prompt resolution.